Allocate behaviour and timing
Functions should be allocated across hardware, firmware, control logic and external services with explicit timing, resource and failure assumptions.
- Define modes, states and transitions.
- Budget execution time, memory, power and bandwidth.
- Specify signal ranges, update rates and diagnostics.
- Identify startup, shutdown and degraded behaviour.
Verify interfaces and real time behaviour
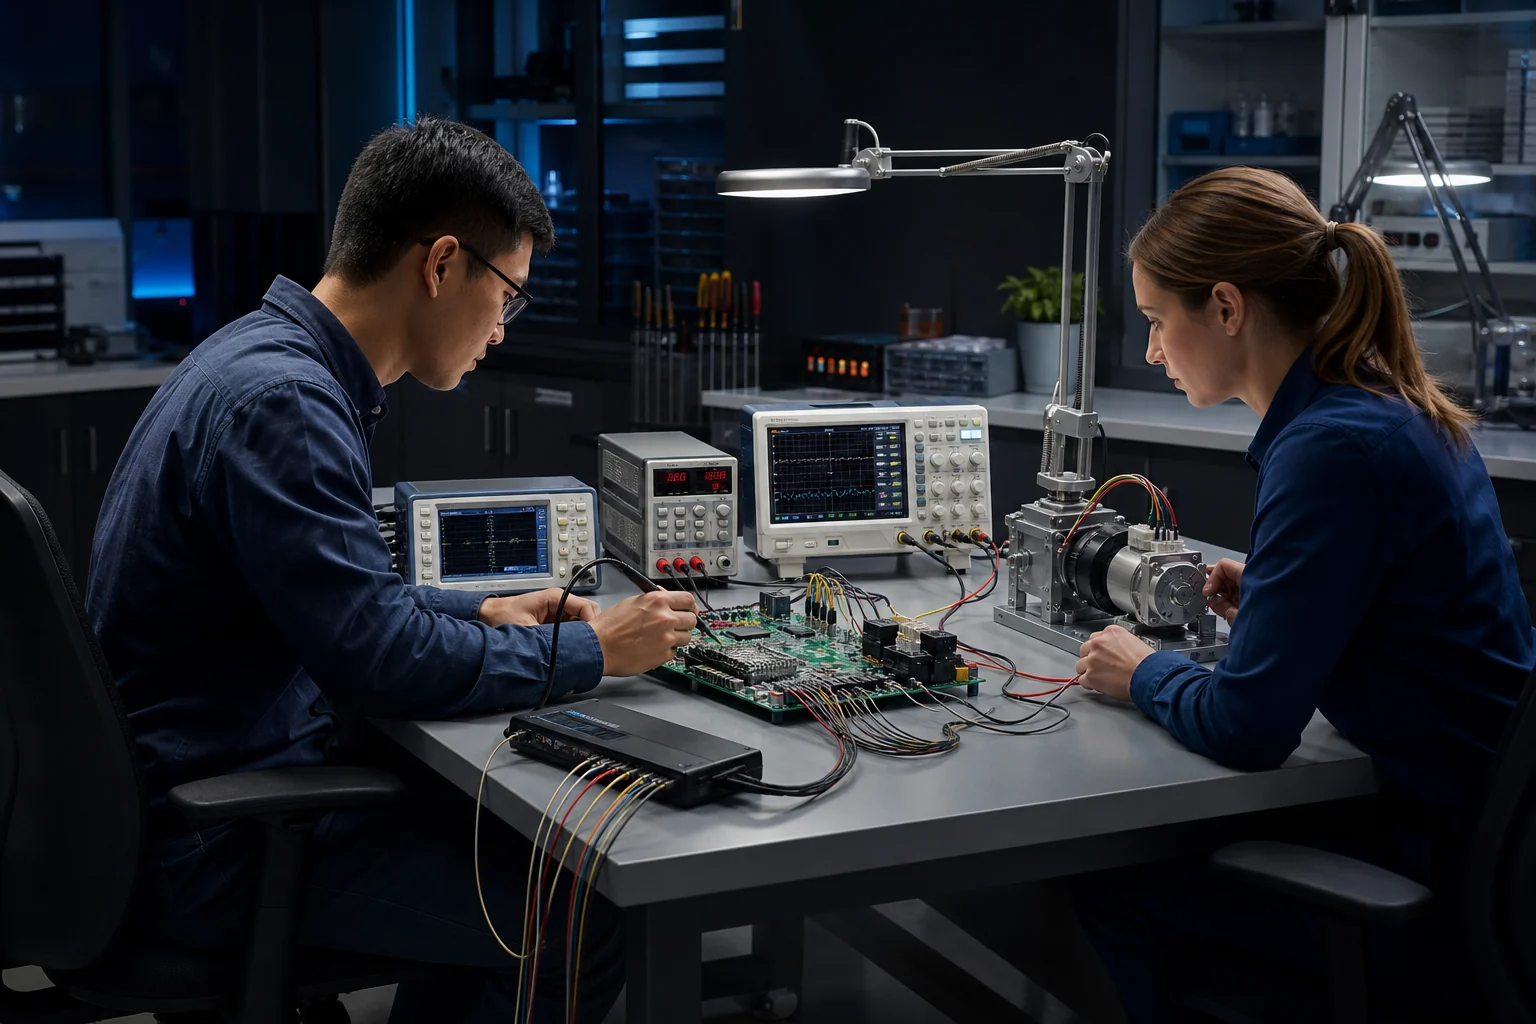
Unit tests alone cannot establish system behaviour. Hardware in the loop, timing measurement, fault injection and communication testing expose interactions that software only testing misses.
- Trace tests to system and software requirements.
- Exercise nominal, boundary and invalid inputs.
- Measure latency, jitter and deadline behaviour.
- Test reset, communication loss and recovery.
Integrate secure development practices
Security activities belong inside the development lifecycle: protecting the development environment, reviewing dependencies, finding vulnerabilities and preparing response capability.
- Control source, build and release provenance.
- Review third party components and update paths.
- Protect secrets and debug interfaces.
- Design logging and vulnerability response before release.
Release a reproducible system configuration
The released product is a specific combination of hardware revision, bootloader, firmware, parameters and manufacturing data. Evidence is meaningful only when tied to that configuration.
- Record toolchain and build configuration.
- Bind firmware to compatible hardware revisions.
- Version calibration and production parameters.
- Retain verification results and known limitations.
Apply the method to the decision, not as a checklist.
The appropriate evidence depends on intended use, technical risk, operating environment, contractual obligations and the authority responsible for acceptance. This guide is educational and does not replace project specific analysis, applicable standards or independent review.